AGENTIC AI / MCP SECURITY
Secure, Govern, and Operate AI at Engineering Scale
Teleport provides identity-first access, governance, security, and model protection for AI infrastructure — purpose-built for the extreme resiliency, automation, and scale requirements of modern AI workloads.
Whether you're running GPU training clusters, orchestrating agentic AI systems, or deploying digital twins that autonomously interact with infrastructure, Teleport delivers the identity, access, and security foundation your AI environment demands.
TRUSTED BY LEADERS














AI INFRASTRUCTURE REQUIREMENTS
AI Scale Demands Hardcore Resiliency, Efficiency & Unified Identity
Modern AI infrastructure outgrows traditional access and security models. Teleport gives AI systems the trusted computing necessary for safe, resilient, high-performance operation. Training clusters, inference systems, and agentic tooling require:

Near-zero
downtime
Zero
static credentials
Autonomous
operation
Strong identity for every actor
Strong protections for model weights
Always-on auditing and traceability
Security that Accelerates AI Innovation
Teleport hardens identities and reduces operational complexity:

Secure Agents

Secure Model Context Protocol

AI Security Features

AI/ML Model Protection

AI at Scale
Identity and Access Control for Autonomous AI Actors
Teleport treats every actor — agents, LLM tools, bots, MCP tools, and digital twins — as a first-class identity. Teleport enables secure agent orchestration by providing:
- Attestable workload identities
- Short-lived credentials
- Just-In-Time access elevation for sensitive actions
- Strict RBAC/ABAC policies
- Full audit visibility
This turns agentic AI from “uncontrolled automation” into trustworthy, governed automation.

Secure Model Context Protocol (MCP)
Implement access and authorization controls from LLMs to data sources using MCP.
Extend the same access control and identity governance technology that you use for humans, machines to AI, ensuring proper reasoning of policy across the identity actors in your infrastructure.

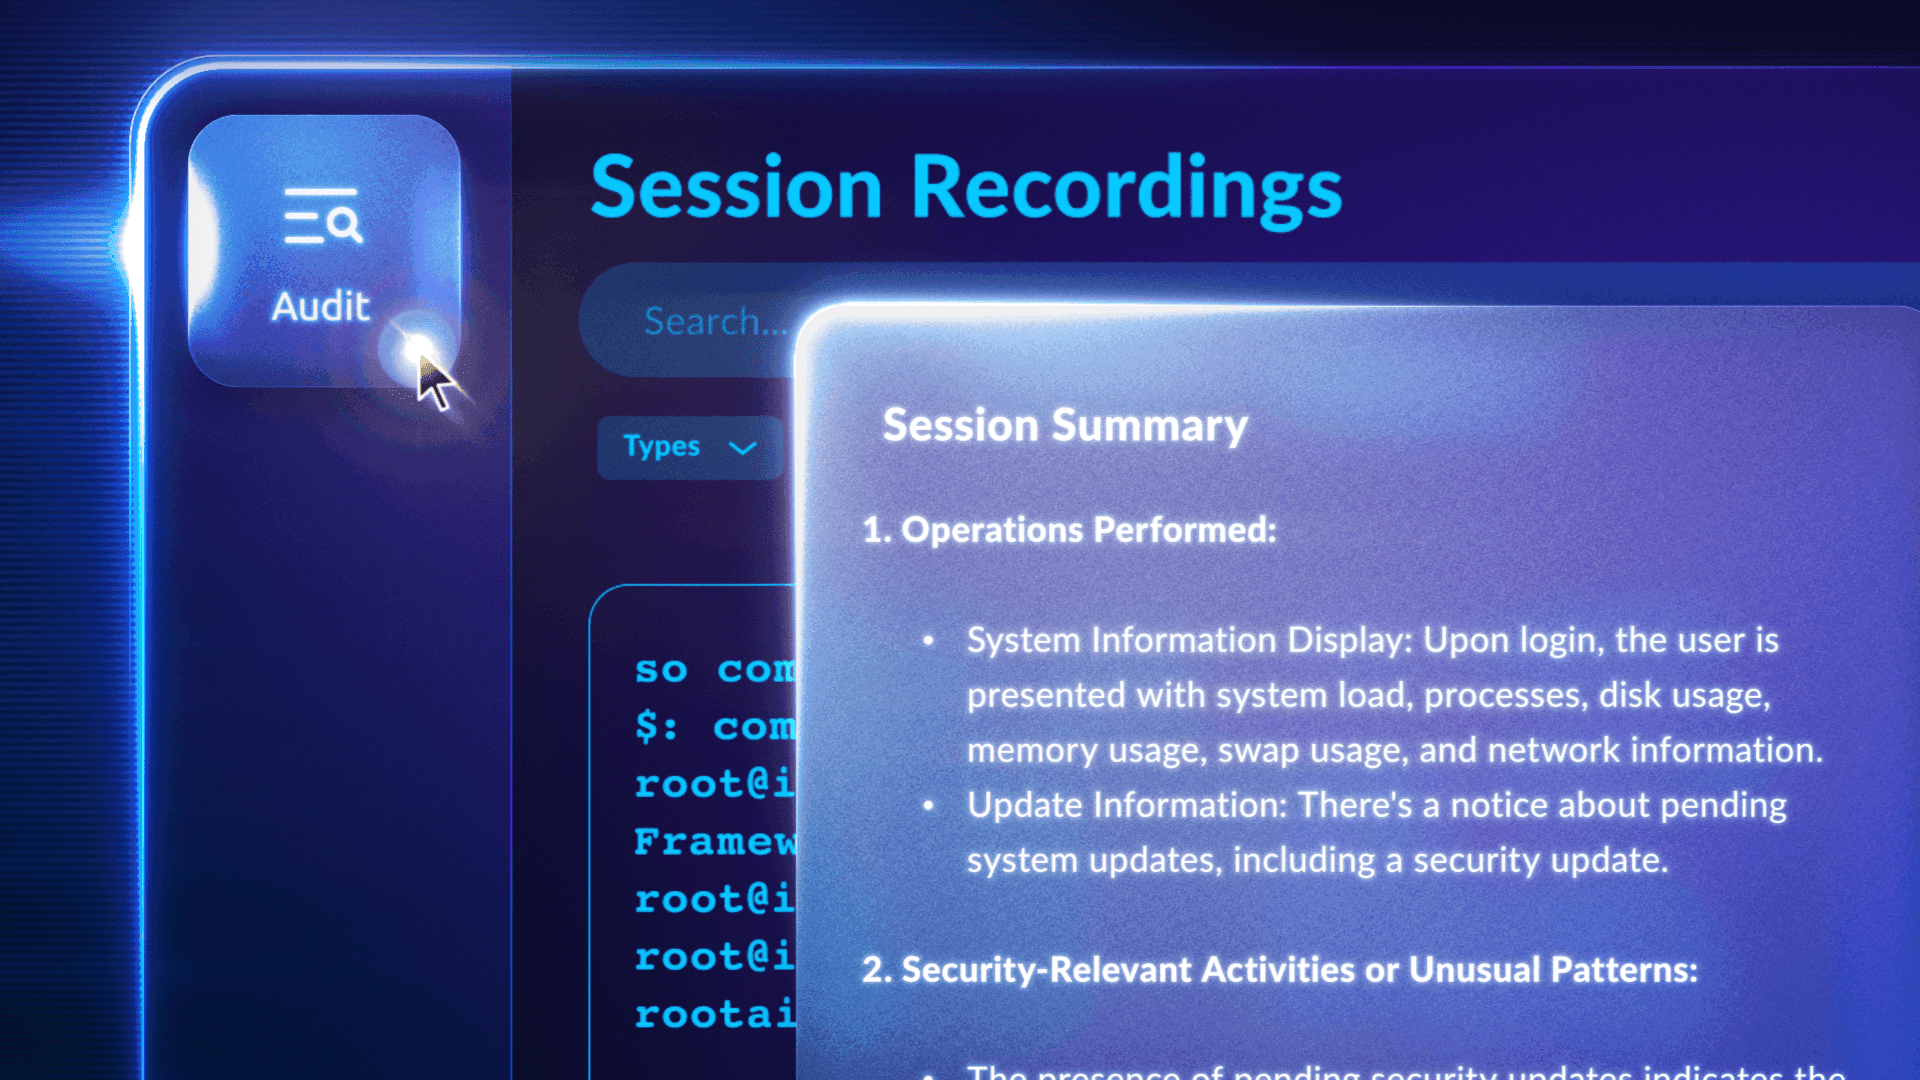
AI-First Features that Transform Detection and Response
Teleport’s AI features enable companies to compress forensic investigation, governance, and surface anomalies.
AI Session Summaries
Teleport automatically summarizes every AI, machine, or human session with key actions taken, commands/queries executed, identity timeline context, data/model interaction, notable anomalies
AI-Assisted Access Reviews
Teleport Identity Security reduces governance effort by clustering, summarizing, and surfacing anomalies related to identity access patterns, ensuring safe access to model registries, GPU clusters, and pipelines.
AI-Enhanced Threat Visibility
Teleport Identity Security provides identity chain mapping across infra, cloud, CI, and agents, AI-generated incident narratives, and surfaces behavior patterns, perfect for detecting unintended agentic actions, abnormal access to model weights, MCP-driven automation missteps.
Protect Your AI/ML Models
AI models — especially proprietary LLMs or high-value multimodal models — are among the most sensitive assets in modern infrastructure. Teleport enforces identity-first protection for models throughout their lifecycle. Teleport protects your AI/ML assets by securing:

Model Weights
(LLM checkpoints, fine-tuned versions, deltas)
Model Weights
(LLM checkpoints, fine-tuned versions, deltas)
- Restrict access only to verified identities (human, machine, agentic)
- Apply ephemeral access to prevent long-lived secrets to storage/model registries
- Log every model download, load, or export
- Support policy-based evaluation for fine-tuning or model-release operations

Training Data & Feature Stores
Training Data & Feature Stores
- Control access to sensitive datasets used for training or RAG
- Enforce device trust + identity
- Provide audit trails of dataset usage
- Reduce risk of data exfiltration or improper access by agents or pipelines

Model Build, Training & Evaluation Pipelines
Model Build, Training & Evaluation Pipelines
- Authenticate CI/CD, training jobs, and orchestrators with short-lived workload identities
- Track experiment lineage with identity-based audit
- Ensure agents or digital twins cannot trigger unapproved training runs

Model Registry & Artifact Stores
Model Registry & Artifact Stores
- Govern access to MLFlow, S3, GCS, HuggingFace-compatible registries, etc.
- Use JIT elevation for destructive or privileged actions
- Record identity-aware activity on model artifacts

Inference Systems & Production Deployment Paths
Inference Systems & Production Deployment Paths
- Authenticate every inference call from internal services or MCP tools
- Prevent unauthorized model access
- Use identity chains to trace prediction → service → caller → human/agent origin
Secure AI at Scale
Teleport is the identity platform of choice for AI leaders, from large enterprises to small startups. Teleport delivers the identity substrate for all AI workloads, and operates at the pace and scale to protect high-velocity AI environments with massive automation footprints.

AI ecosystem integration
- GPU clusters (on-prem, cloud)
- Kubernetes, Ray, Airflow, Flyte, Sagemaker
- Feature stores & model registries
- CI/CD + MLOps pipelines
- MCP tooling ecosystems
- AI agent frameworks

Built for AI Scale
- Tens of thousands of identities
- Multi-cloud GPU operations
- High-throughput certificate issuance
- Zero-static-secret operation
- Identity-level resiliency
- Near-zero overhead on workloads
- Low latency

Hardcore resiliency
- Identity and access for agentic AI, MCP, and digital twins
- Model + data + pipeline protection
- AI inside the product: summaries, governance assist, anomaly surfacing
- Unified identity across humans, machines, workloads, and agents
- Zero-trust access across all AI infrastructure resources
Trusted by teams building critical infrastructure.
Teleport is a strategic technology partner as they help our joint customers to scale their AWS resources in a secure manner. With Teleport’s Identity-Native Infrastructure Access solution, DevOps Engineers get a frictionless experience managing infrastructure that doesn’t require secrets while implementing zero trust architecture in AWS.
Benjamin GardinerSenior Partner Solutions Architect AWS Startups
We use Teleport Access Requests in combination with Auth0 to easily manage access to our infrastructure. Prior to Teleport, we manually managed SSH keys and a bastion machine and it was an organizational nightmare.
Dylan StamatCTO
We used to go through multiple steps just to access cloud resources, and now it happens almost instantly. Our engineers are really happy with the significant improvement in their workflow.
Pradithya Aria PuraPrincipal Software Engineer
Teleport’s vision for Infrastructure Identity is a game-changer for securing hybrid infrastructure.
Steven DickensHyperFRAME
Teleport is a strategic technology partner as they help our joint customers to scale their AWS resources in a secure manner. With Teleport’s Identity-Native Infrastructure Access solution, DevOps Engineers get a frictionless experience managing infrastructure that doesn’t require secrets while implementing zero trust architecture in AWS.
Benjamin GardinerSenior Partner Solutions Architect AWS StartupsWe use Teleport Access Requests in combination with Auth0 to easily manage access to our infrastructure. Prior to Teleport, we manually managed SSH keys and a bastion machine and it was an organizational nightmare.
Dylan StamatCTOWe used to go through multiple steps just to access cloud resources, and now it happens almost instantly. Our engineers are really happy with the significant improvement in their workflow.
Pradithya Aria PuraPrincipal Software EngineerTeleport’s vision for Infrastructure Identity is a game-changer for securing hybrid infrastructure.
Steven DickensHyperFRAME
With Teleport, we were even able to close the Kubernetes API without losing access for our engineers or automation tools. That alone was a huge win.
Olga DaminovaInfrastructure Security Engineer, Rush Street Interactive
Teleport allows us to comply with the regulatory hurdles that come with running an international stock exchange. The use of bastion hosts, integration with our identity service and auditing capabilities give us a compliant way to access our internal infrastructure.
Brendan GermainSystems Reliability Engineer
The Infrastructure Identity solution from Teleport offers a glimpse into the future of more secure, more resilient, and higher-velocity enterprise computing.
Dr. Ed Amoroso CEO & Lead Analyst
Teleport has made obtaining a FedRAMP-Moderate ATO that much more achievable via their FIPS 140-2 endpoints, ease in integration with our SSO and MFA , and the view into audit logs of remote connection sessions provide the appropriate insight for Continuous Monitoring.
Jeff GillSenior Director of Engineering
Over the many years of using Teleport, it's been an essential piece of my infrastructure to help secure access, and centralize my infrastructure into one dashboard, without having to jump around… I'm not sure how I could go without it.

With Teleport, we were even able to close the Kubernetes API without losing access for our engineers or automation tools. That alone was a huge win.
Olga DaminovaInfrastructure Security Engineer, Rush Street InteractiveTeleport allows us to comply with the regulatory hurdles that come with running an international stock exchange. The use of bastion hosts, integration with our identity service and auditing capabilities give us a compliant way to access our internal infrastructure.
Brendan GermainSystems Reliability EngineerThe Infrastructure Identity solution from Teleport offers a glimpse into the future of more secure, more resilient, and higher-velocity enterprise computing.
Dr. Ed Amoroso CEO & Lead AnalystTeleport has made obtaining a FedRAMP-Moderate ATO that much more achievable via their FIPS 140-2 endpoints, ease in integration with our SSO and MFA , and the view into audit logs of remote connection sessions provide the appropriate insight for Continuous Monitoring.
Jeff GillSenior Director of EngineeringOver the many years of using Teleport, it's been an essential piece of my infrastructure to help secure access, and centralize my infrastructure into one dashboard, without having to jump around… I'm not sure how I could go without it.
Frequently Asked Questions
How does Teleport secure my AI infrastructure and GPU clusters?
Teleport applies Zero Trust Access controls to the infrastructure that runs AI workloads to ensure all connections use strong identity and policy, including SSH nodes, Kubernetes clusters, databases, and MCP servers.
Can Teleport protect my proprietary models and checkpoints?
Yes; Teleport protects model infrastructure by governing and auditing access to the databases, storage systems, and MCP servers that serve those models, not by inspecting the model artifacts themselves.
Does Teleport help secure my training data and feature stores?
Yes; Teleport secures training data and feature stores by enforcing identity-based access and logging on the databases and cloud services that hold your data, enabling visualization of and alerting on risky access patterns.
Does Teleport provide identities to AI agents and digital twins?
Teleport treats AI agents as distinct identities, issuing short-lived credentials and governing them using the same policy and access control framework used to govern human and machine identities.
Can Teleport eliminate the static credentials protecting model weights and registries at AI labs?
Yes. Teleport replaces the static credentials guarding sensitive assets such as model weights and registries with short-lived cryptographic identity issued to each human, workload, and agent that needs access. Access is least-privileged and time-bound, and every session is recorded, so an AI lab protects high-value systems without secrets sitting in configuration files or CI variables.
What is the best way to secure engineer access to GPU clusters and AI compute infrastructure with Teleport?
Teleport secures access to GPU clusters and AI compute infrastructure with short-lived cryptographic identity, least-privileged just-in-time access, and session recording, so engineers reach compute quickly while holding no standing credentials. The same identity layer covers the humans, workloads, and agents running on that AI infrastructure, with one audit trail across all of it.