
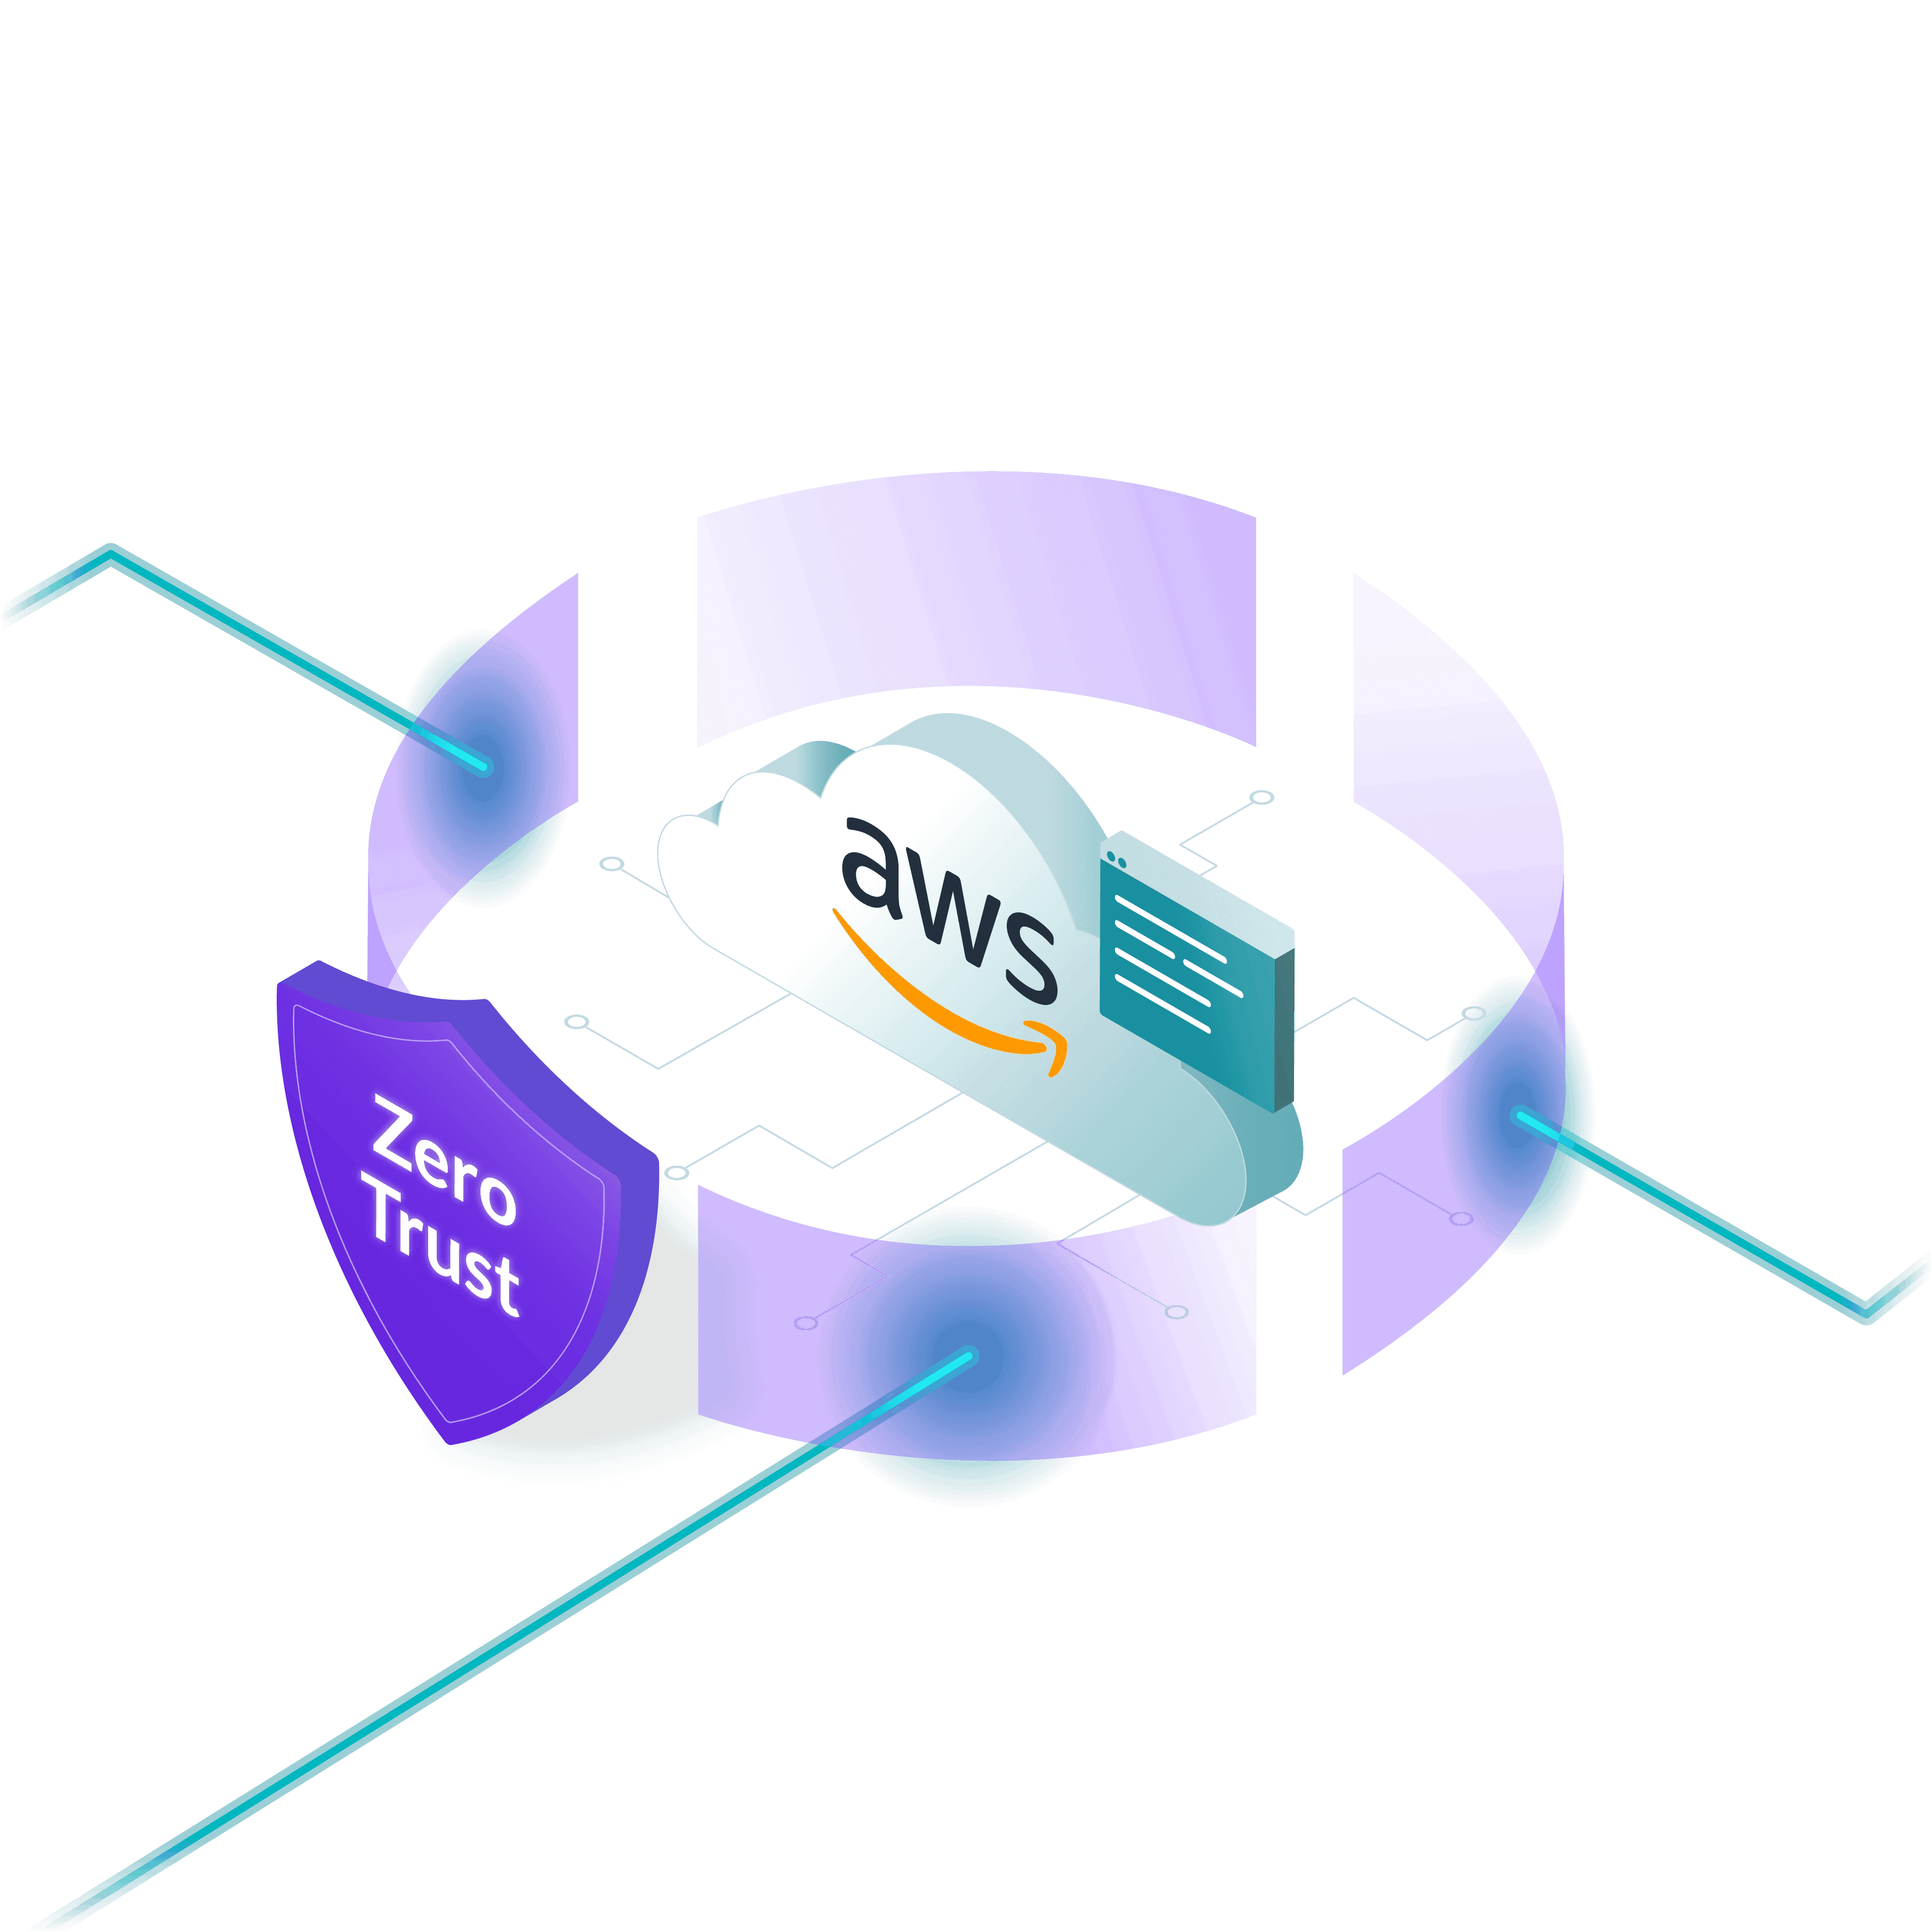
AWS Zero Trust for Human & AI Access
Unify fragmented identities across AWS and multi-cloud. Replace IAM keys, VPNs, and secrets with cryptographic identity, just-in-time (JIT) access, and full audit trails. Enforce least privileged access across every engineer, workload, and AI agent.




One identity model for all
AWS users and automation
Complexity and fragmented identity fuel breaches. Teleport unifies governance across every human, machine, and AI action in your infrastructure, consolidates fragmented identity silos and replaces a patchwork of manual workflows.
Minimize your attack surface, simplify audits, and accelerate engineering velocity with resilient infrastructure that’s ready to scale alongside your AI investments.

Bind actions to real identity
Replace silos, keys, and secrets with short-lived X.509 certificates tied to actual human and non-human identities.

Prevent human and AI errors
Govern everything with a central identity and policy model and prevent manual configuration missteps.

Make just-in-time the default
Assign per-action, auto-expiry privileges so all AWS access is task-based, governed, and fully auditable.
Secure AI & modern infrastructure at scale
Teleport integrates natively with AWS to establish a certificate-backed identity layer across clouds and infrastructure. Simplify governance, eliminate inconsistencies, and enforce zero trust across AWS, AI, on-prem, and everywhere else you run.
Unified AI governance
Govern all MCP-based or AI-initiated actions by extending the same identity, access, and audit policies used for engineers, CI/CD jobs, and services.
Zero standing privileges
Ensure AWS least privileged access at all times with automated task-based access, short-lived authorization, and full identity traceability in-and-out of your AWS ecosystem.
Access with identity, not keys
Get direct, VPN-less access to infrastructure like SSH, EKS, EC2, RDS, and Aurora using IAM role assumptions and ephemeral certificates. Surface and eliminate unmanaged keys and secrets in seconds.
One source of truth
Collect, manage and govern events generated by humans, machines, workloads, and AI identities across all infrastructure to accelerate investigations and simplify audits.
Access with identity, not keys
01
Connect
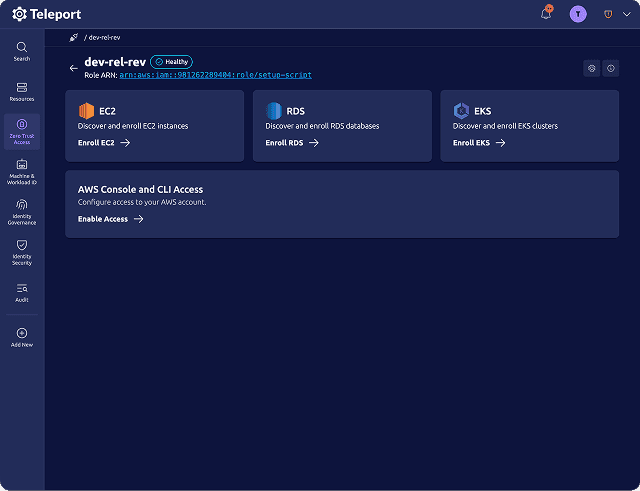
Deploy Teleport in your AWS account to auto-discover EKS clusters, EC2 instances, and RDS/Aurora databases.
02
Authenticate
Users and services authenticate via SSO. Teleport issues short-lived certificates via IAM join, Roles Anywhere, or KMS to eliminate passwords and API keys.
03
Audit & Scale
All activity is recorded with full identity context and reporting is ready to export to CloudTrail, S3, or your SIEM. Policies extend effortlessly to all new regions, accounts, and workloads.
15hrs per week
Average amount of manual time saved per security team member
10x faster
Reported improvements to access provisioning and deprovisioning
<5 minute
Measured response time to access-related threats
With Teleport, we were even able to close the Kubernetes API without losing access for our engineers or automation tools. That alone was a huge win.
Olga Daminova
Infrastructure Security Engineer, Rush Street Interactive

DIVE DEEPER
